How to Build a Risk-Based SNA Detection in Splunk
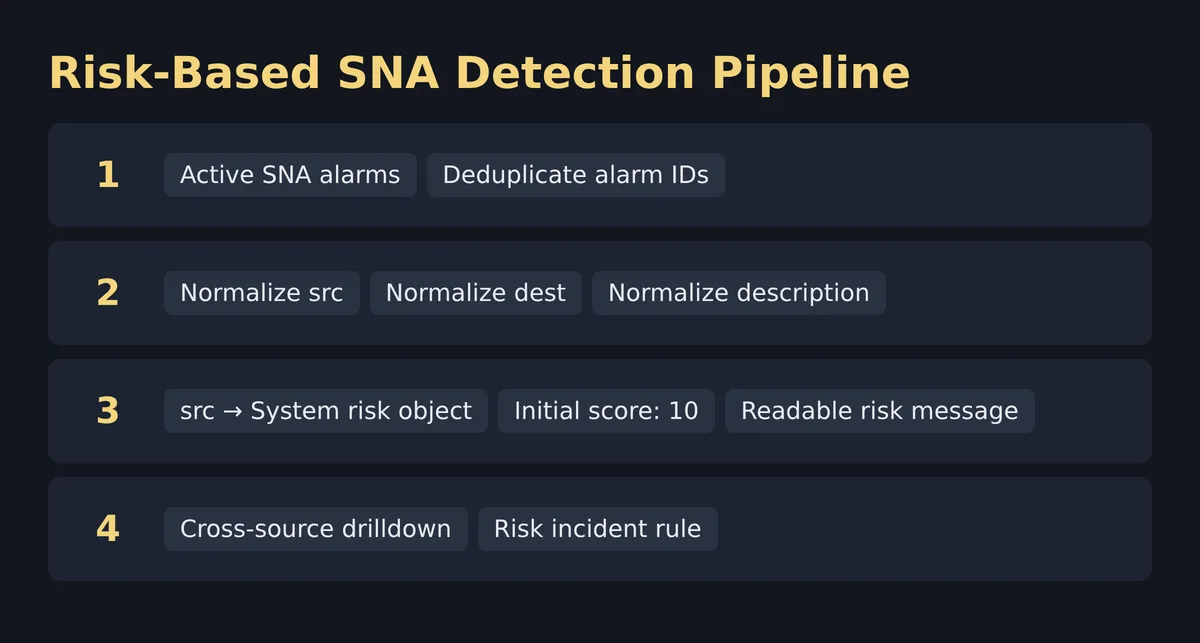
A risk-based SNA detection in Splunk should turn each active Cisco Secure Network Analytics alarm into evidence attached to a stable entity, not another isolated alert. Normalize the source, destination, and description fields; remove duplicate alarm IDs; write the source system to Splunk Enterprise Security’s risk index; and preserve enough network context for an analyst to investigate. According to Cisco (2026), its published design used the normalized source IP as a System risk object with an initial score of 10, explicitly treating that score as an observation rather than proof of compromise. ...